Question: In the context of secure coding, what is the purpose of using prepared statements for database queries?
Answer:
Prepared statements help prevent SQL Injection attacks by separating SQL code from user input.
MCQ: In the context of secure coding, what is the purpose of using prepared statements for database queries?
Explanation:
Prepared statements help prevent SQL Injection attacks by separating SQL code from user input.
Discuss a Question
Related Questions
- 1. What security measure involves encrypting sensitive data before storing or transmitting it in a web application?
- 2. How does regular software and framework updating contribute to secure coding?
- 3. What is the purpose of using secure coding libraries and frameworks in web application development?
- 4. How does session management contribute to secure coding in web applications?
- 5. What is the significance of using strong, unique passwords and proper password storage in secure coding?
- 6. How can secure error handling contribute to secure coding practices?
- 7. What is the purpose of code reviews in the context of secure coding?
- 8. How can static code analysis tools contribute to secure coding in web applications?
- 9. Why is it important to perform code reviews and static code analysis regularly throughout the development lifecycle?
- 10. What role does the use of secure coding guidelines play in the code review process?
You may be interested in:
Web Security MCQsRecently Added Articles
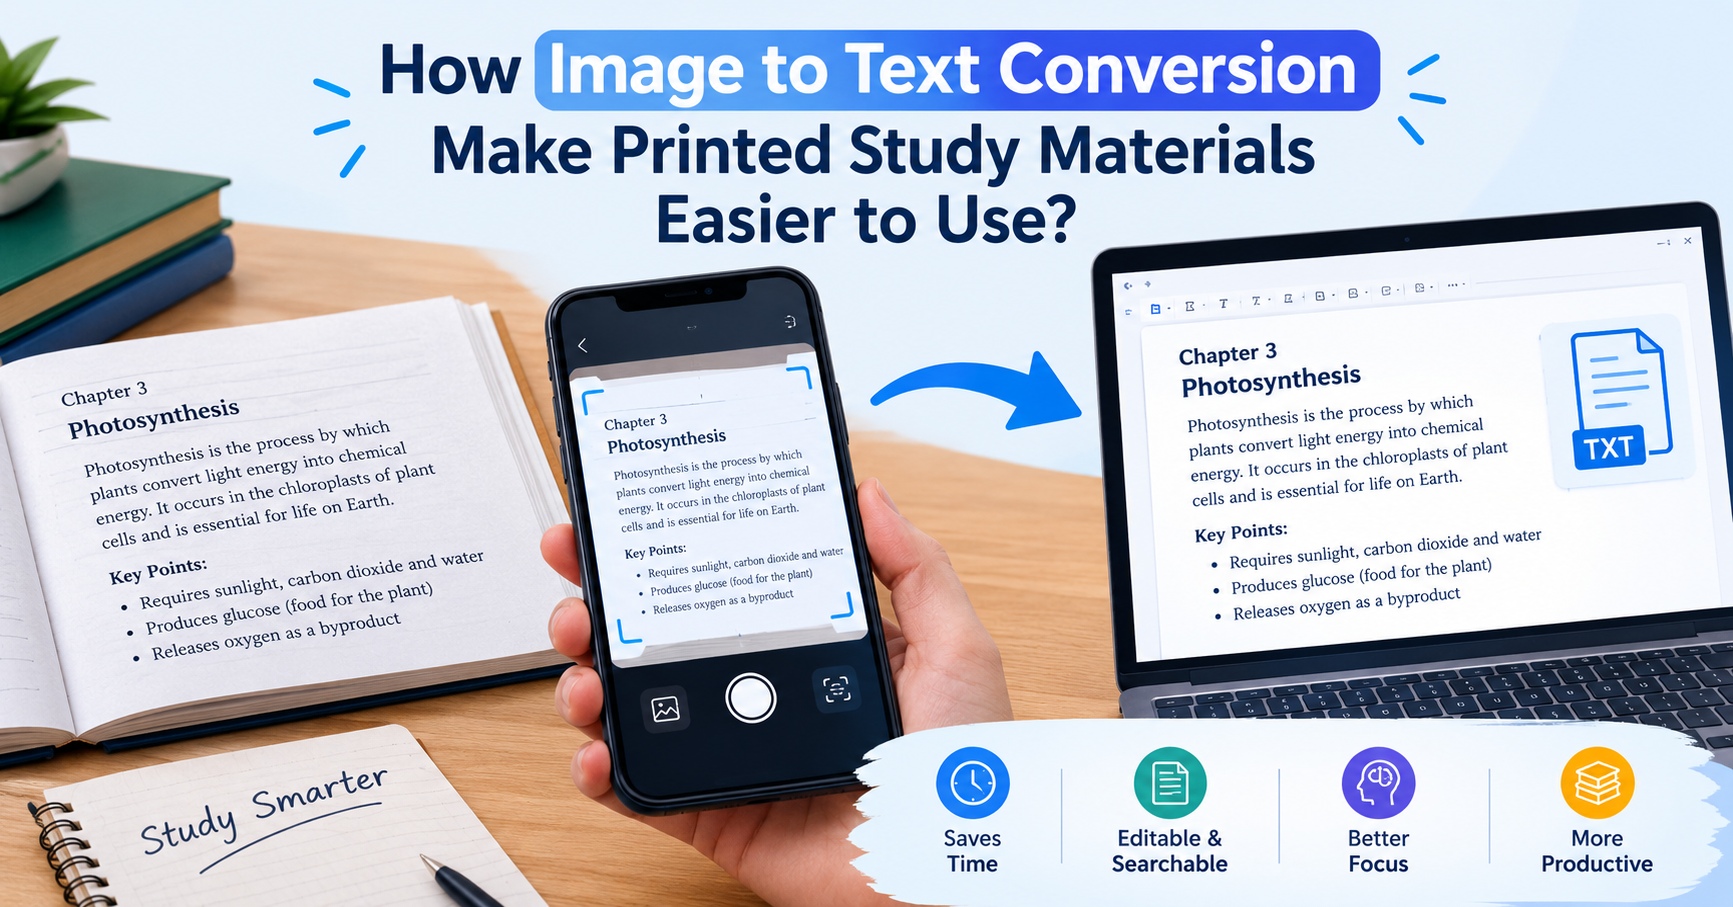
How Image to Text Conversion Make Printed Study Materials Easier to Use?
Last updated on: October 23, 2026Posted by: ExamRadar
7 Best Online Exam Makers for Teachers, Schools, and Businesses
Last updated on: October 21, 2026Posted by: ExamRadar
How to pick a Bintan resort when you’ve only got 48 hours
Last updated on: September 23, 2026Posted by: ExamRadar
Features to Look for While Choosing the Best Automation Tool
Last updated on: July 15, 2026Posted by: ExamRadar
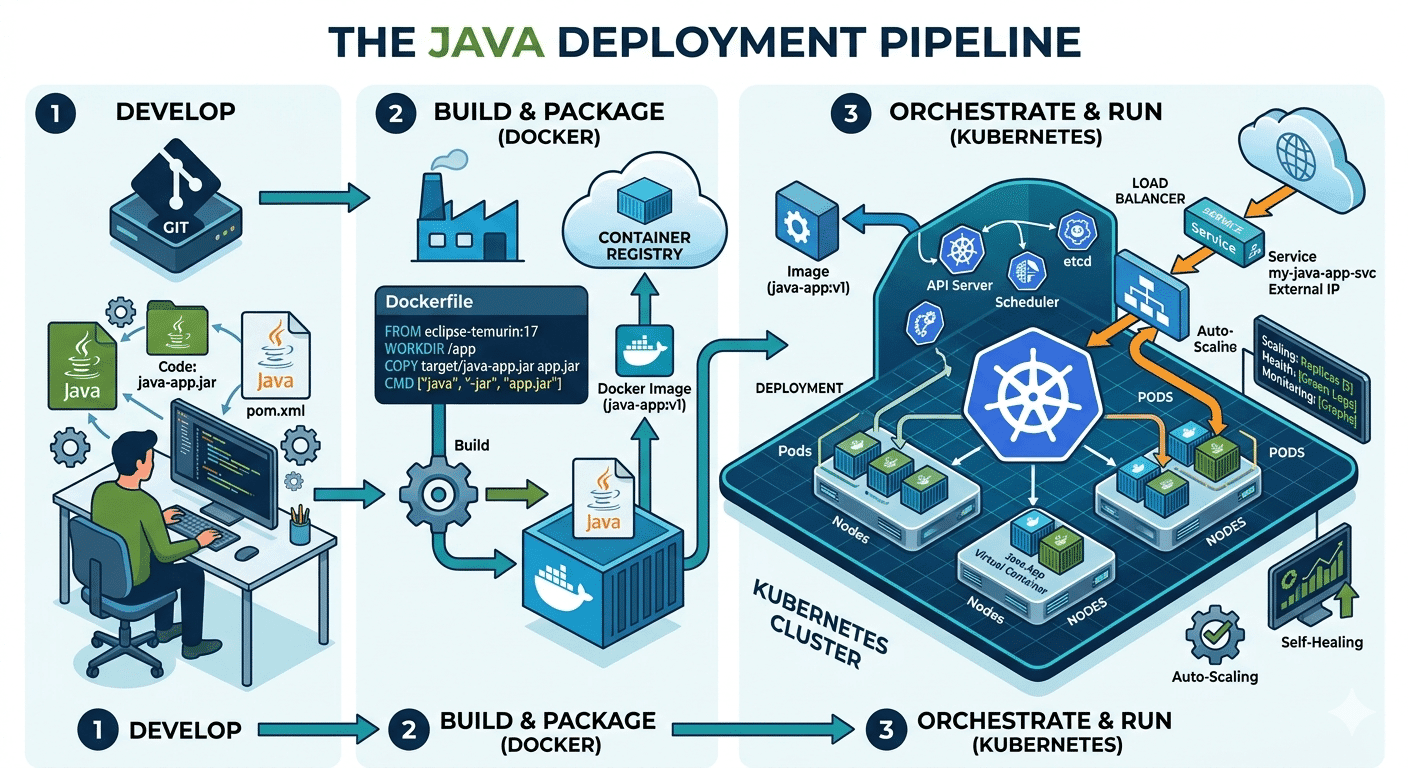
How Do Java Development Teams Use Docker and Kubernetes to Deploy Applications?
Last updated on: April 24, 2026Posted by: ExamRadar
AI vs Machine Learning: Key Differences Every Professional Should Know
Last updated on: February 13, 2026Posted by: ExamRadar
Office Cleaning Services That Elevate Sydney Offices
Last updated on: February 11, 2026Posted by: ExamRadar