Question: What security risks does the Cross-Origin-Read-Time (CORT) header address, and how does it mitigate them?
Answer:
The Cross-Origin-Read-Time (CORT) header addresses risks like timing attacks on cross-origin resources. It mitigates these risks by controlling the timing information shared with the web page.
MCQ: What security risks does the Cross-Origin-Read-Time (CORT) header address, and how does it mitigate them?
Explanation:
The Cross-Origin-Read-Time (CORT) header addresses risks like timing attacks on cross-origin resources. It mitigates these risks by controlling the timing information shared with the web page.
Discuss a Question
Related Questions
- 1. How does the Cross-Origin-Resource-Policy (CORP) header help mitigate Cross-Site Scripting (XSS) attacks?
- 2. What security purpose does the Clear-Site-Data header serve, and how does it contribute to privacy and security?
- 3. How does the Public-Key-Pins (HPKP) header enhance security in web applications?
- 4. What risks does the X-Permitted-Cross-Domain-Policies header address, and how does it mitigate them?
- 5. How does the HTTP Content-Security-Policy header contribute to web security, and what security controls does it provide?
- 6. What security considerations should developers keep in mind when configuring the Access-Control-Allow-Origin header?
- 7. How does the HTTP Strict-Transport-Security (HSTS) preload mechanism enhance security, and what considerations should be taken into account when using it?
- 8. How does the HTTP Expect-CT header contribute to the security of web applications, and what risks does it address?
- 9. How can the HTTP Referrer-Policy header be configured to balance privacy and functionality in web applications?
- 10. How does the HTTP Feature-Policy header help control the availability of specific web features, and what security benefits does it provide?
You may be interested in:
Web Security MCQsRecently Added Articles
How to pick a Bintan resort when you’ve only got 48 hours
Last updated on: September 23, 2026Posted by: ExamRadar
Features to Look for While Choosing the Best Automation Tool
Last updated on: July 15, 2026Posted by: ExamRadar
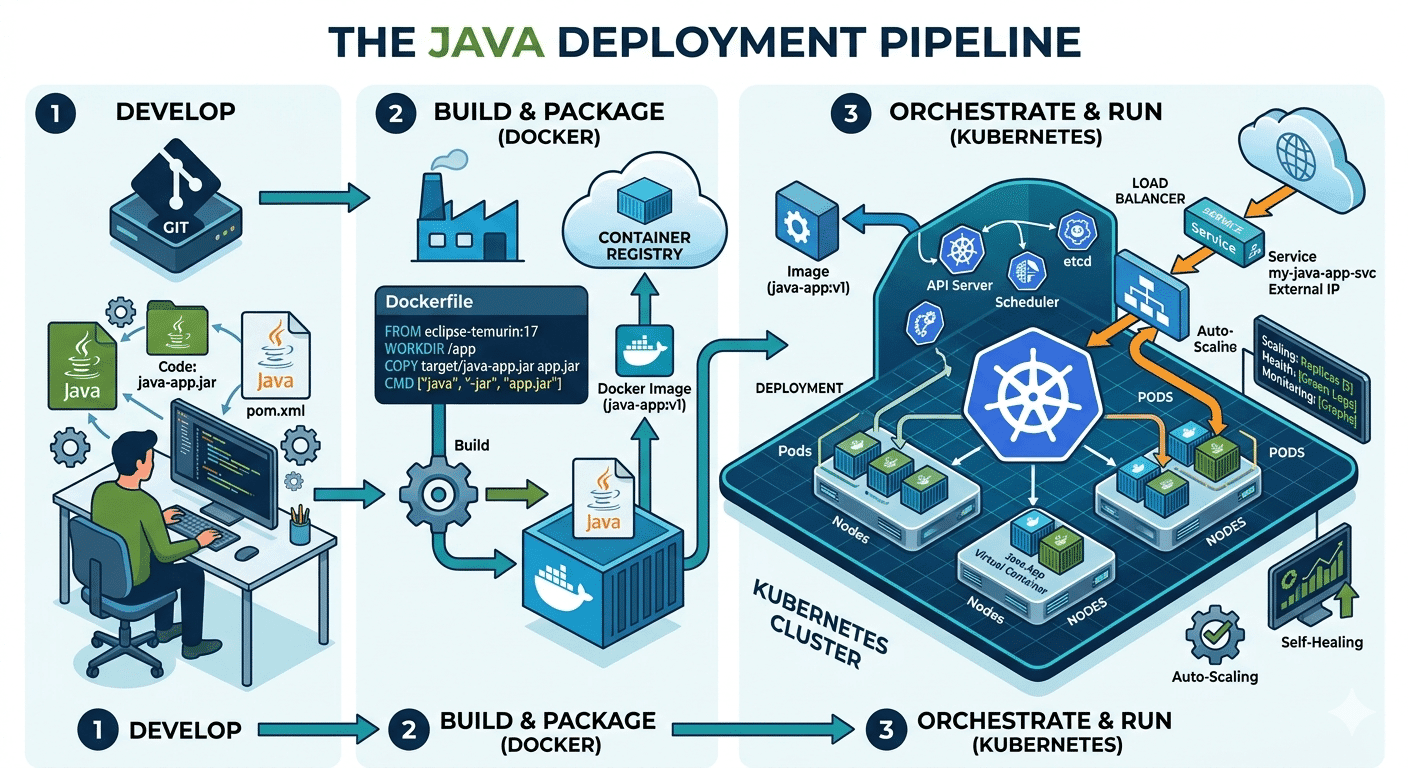
How Do Java Development Teams Use Docker and Kubernetes to Deploy Applications?
Last updated on: April 24, 2026Posted by: ExamRadar
AI vs Machine Learning: Key Differences Every Professional Should Know
Last updated on: February 13, 2026Posted by: ExamRadar
Office Cleaning Services That Elevate Sydney Offices
Last updated on: February 11, 2026Posted by: ExamRadar
What You Actually Learn About Exam Patterns From RBI Grade B Previous Year Papers?
Last updated on: February 9, 2026Posted by: ExamRadar
Mental Health Support That’s Closer Than You Think
Last updated on: January 7, 2026Posted by: ExamRadar
Transform Your Home’s Exterior with Columbus roofing company
Last updated on: November 27, 2025Posted by: ExamRadar