Question: How can attackers use "non-randomized modules with DEP emulation" in DEP bypass?
Answer:
"Non-randomized modules with DEP emulation" in DEP bypass attacks involve identifying modules that are not subject to DEP and combining this information with DEP emulation to find vulnerabilities in DEP implementation.
MCQ: How can attackers use "non-randomized modules with DEP emulation" in DEP bypass?
Explanation:
"Non-randomized modules with DEP emulation" in DEP bypass attacks involve identifying modules that are not subject to DEP and combining this information with DEP emulation to find vulnerabilities in DEP implementation.
Discuss a Question
Related Questions
- 1. What is the significance of "return-oriented programming with ASLR and DEP bypass" in web security?
- 2. What does ROP stand for in the context of web security?
- 3. What is a "ROP gadget" in the context of web security?
- 4. How are ROP gadgets used in the exploitation of native compiled applications?
- 5. What role do "return instructions" play in ROP gadgets?
- 6. Why are ROP gadgets considered a powerful technique in exploitation?
- 7. What is the primary advantage of using ROP gadgets over traditional code injection techniques?
- 8. In ROP chains, what is the purpose of chaining together multiple gadgets?
- 9. How does a typical ROP chain work in the context of exploitation?
- 10. What is the significance of "gadget farming" in ROP exploitation?
You may be interested in:
Web Security MCQsRecently Added Articles
5 Best Amazon Advertising Agencies for Growing Brands
Last updated on: November 6, 2026Posted by: ExamRadar
How Image to Text Conversion Make Printed Study Materials Easier to Use?
Last updated on: October 23, 2026Posted by: ExamRadar
7 Best Online Exam Makers for Teachers, Schools, and Businesses
Last updated on: October 21, 2026Posted by: ExamRadar
How to pick a Bintan resort when you’ve only got 48 hours
Last updated on: September 23, 2026Posted by: ExamRadar
Features to Look for While Choosing the Best Automation Tool
Last updated on: July 15, 2026Posted by: ExamRadar
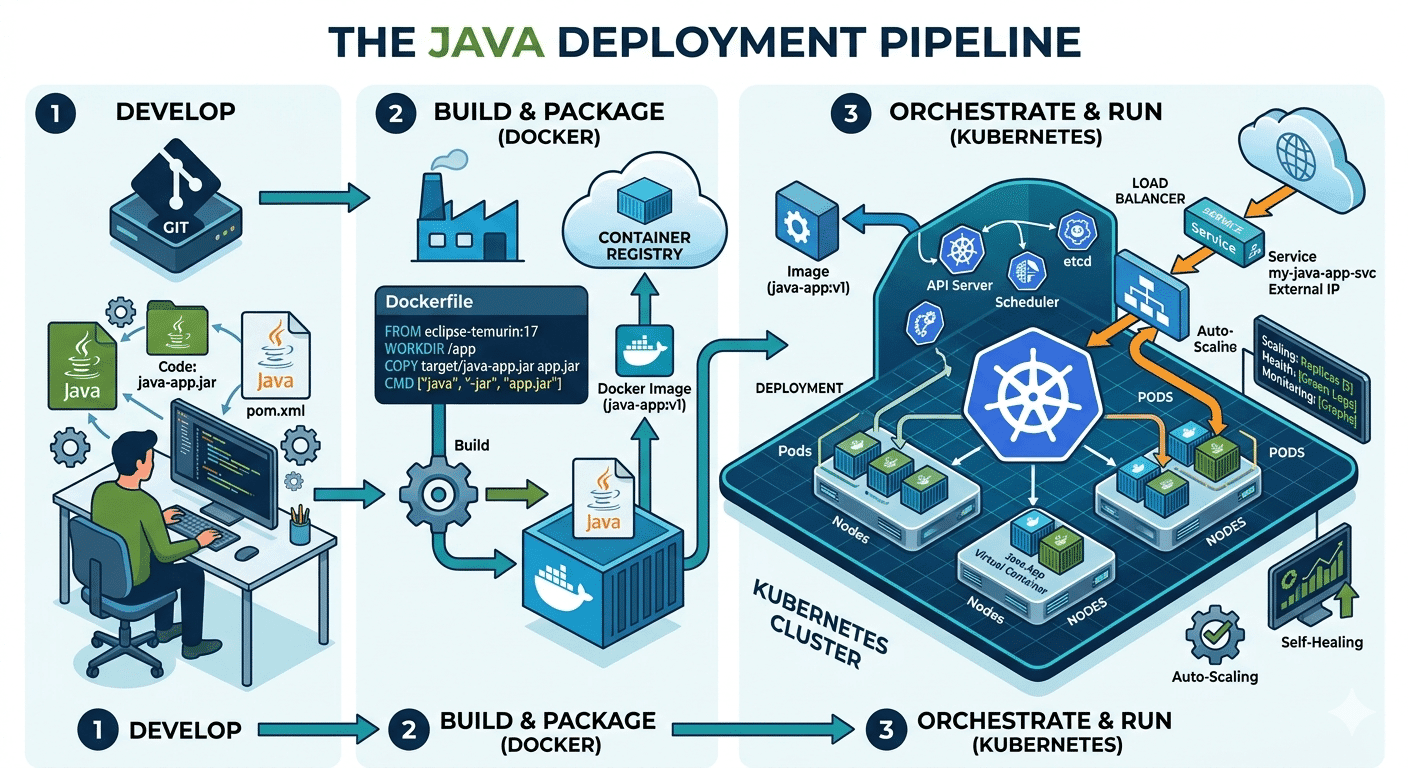
How Do Java Development Teams Use Docker and Kubernetes to Deploy Applications?
Last updated on: April 24, 2026Posted by: ExamRadar
AI vs Machine Learning: Key Differences Every Professional Should Know
Last updated on: February 13, 2026Posted by: ExamRadar