Question: How can implementing security-aware third-party integrations contribute to the prevention of both XSS and CSRF attacks at the architectural level?
Answer:
Implementing security-aware third-party integrations at the architectural level is crucial to ensure that external components adhere to security best practices, mitigating both XSS and CSRF vulnerabilities by reducing the risk introduced by external dependencies.
MCQ: How can implementing security-aware third-party integrations contribute to the prevention of both XSS and CSRF attacks at the architectural level?
Explanation:
Implementing security-aware third-party integrations at the architectural level is crucial to ensure that external components adhere to security best practices, mitigating both XSS and CSRF vulnerabilities by reducing the risk introduced by external dependencies.
Discuss a Question
Related Questions
- 1. Why is it important to conduct regular security audits and assessments at the architectural level to identify and address potential XSS and CSRF vulnerabilities?
- 2. How can attackers exploit the lack of security audits and assessments at the architectural level to launch XSS and CSRF attacks?
- 3. How can implementing a bug bounty program contribute to the detection and resolution of XSS and CSRF vulnerabilities at the architectural level?
- 4. Why is it important to provide security training and awareness programs for developers at the architectural level to reduce the risk of XSS and CSRF vulnerabilities?
- 5. How can attackers exploit the lack of security training and awareness at the architectural level to launch XSS and CSRF attacks?
- 6. What is a security misconfiguration in the context of web application architecture?
- 7. Why are security misconfigurations considered a significant security risk in web applications?
- 8. Which of the following is an example of a common security misconfiguration?
- 9. How can attackers exploit security misconfigurations related to default settings in web applications?
- 10. What is the impact of security misconfigurations on the confidentiality of sensitive information?
You may be interested in:
Web Security MCQsRecently Added Articles
5 Best Amazon Advertising Agencies for Growing Brands
Last updated on: November 6, 2026Posted by: ExamRadar
How Image to Text Conversion Make Printed Study Materials Easier to Use?
Last updated on: October 23, 2026Posted by: ExamRadar
7 Best Online Exam Makers for Teachers, Schools, and Businesses
Last updated on: October 21, 2026Posted by: ExamRadar
How to pick a Bintan resort when you’ve only got 48 hours
Last updated on: September 23, 2026Posted by: ExamRadar
Features to Look for While Choosing the Best Automation Tool
Last updated on: July 15, 2026Posted by: ExamRadar
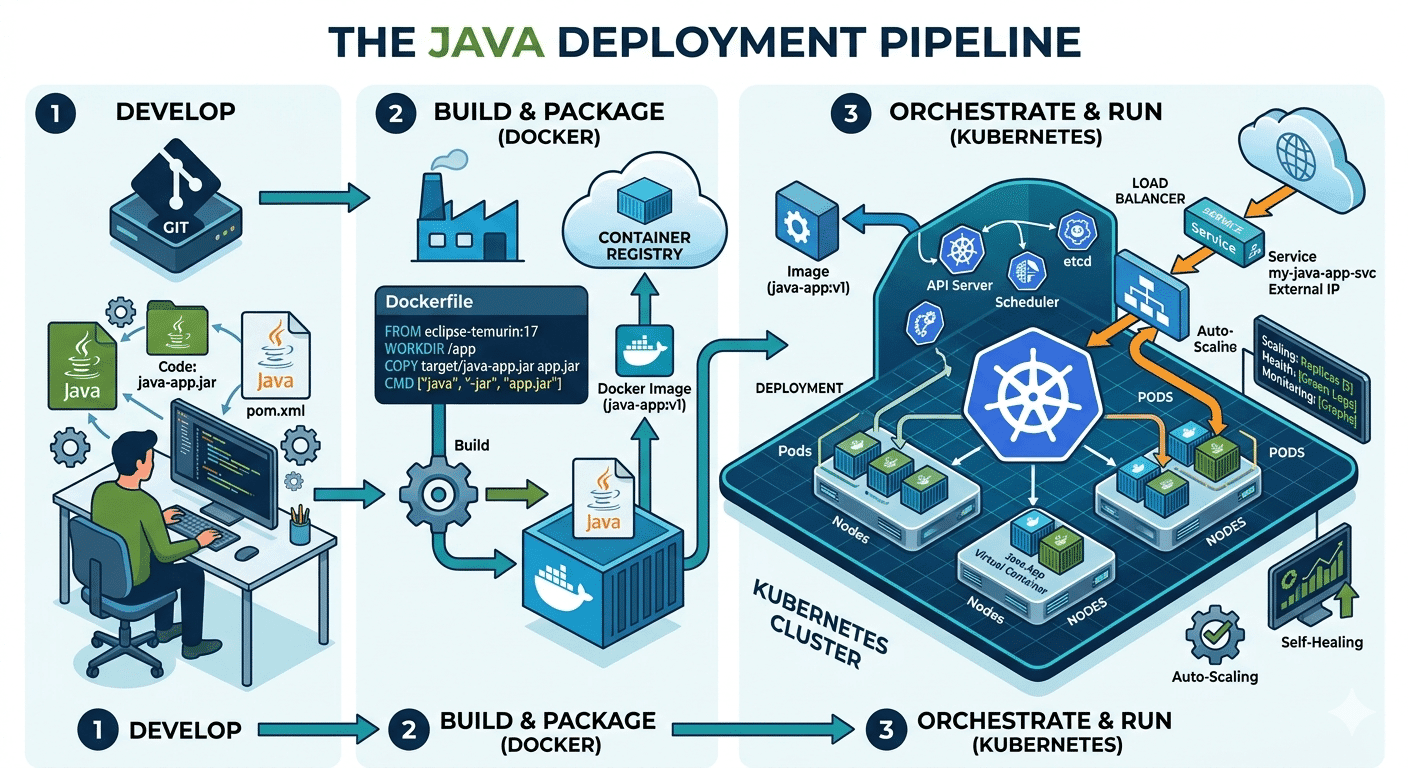
How Do Java Development Teams Use Docker and Kubernetes to Deploy Applications?
Last updated on: April 24, 2026Posted by: ExamRadar
AI vs Machine Learning: Key Differences Every Professional Should Know
Last updated on: February 13, 2026Posted by: ExamRadar