Question: How can attackers use DOM-based XSS to execute malicious scripts?
Answer:
Attackers use DOM-based XSS to execute malicious scripts by injecting them directly into the Document Object Model (DOM) of a web page, allowing them to run in the user's browser.
MCQ: How can attackers use DOM-based XSS to execute malicious scripts?
Explanation:
Attackers use DOM-based XSS to execute malicious scripts by injecting them directly into the Document Object Model (DOM) of a web page, allowing them to run in the user's browser.
Discuss a Question
Related Questions
- 1. What is the purpose of HTML injection in client-side attacks?
- 2. How do attackers exploit Cross-Site Request Forgery (CSRF) in client-side attacks?
- 3. In client-side attacks, what is the purpose of stealing user cookies?
- 4. What is the primary risk associated with insecure direct object references (IDOR) in client-side attacks?
- 5. How can attackers exploit insecure deserialization in client-side attacks?
- 6. What is the purpose of clickjacking in client-side attacks?
- 7. What is the role of content spoofing in client-side attacks?
- 8. What is a common technique for preventing Cross-Site Scripting (XSS) in client-side code?
- 9. How do attackers leverage man-in-the-middle attacks for client-side exploits?
- 10. In client-side attacks, what is the purpose of obfuscation techniques?
You may be interested in:
Web Security MCQsRecently Added Articles
5 Best Amazon Advertising Agencies for Growing Brands
Last updated on: November 6, 2026Posted by: ExamRadar
How Image to Text Conversion Make Printed Study Materials Easier to Use?
Last updated on: October 23, 2026Posted by: ExamRadar
7 Best Online Exam Makers for Teachers, Schools, and Businesses
Last updated on: October 21, 2026Posted by: ExamRadar
How to pick a Bintan resort when you’ve only got 48 hours
Last updated on: September 23, 2026Posted by: ExamRadar
Features to Look for While Choosing the Best Automation Tool
Last updated on: July 15, 2026Posted by: ExamRadar
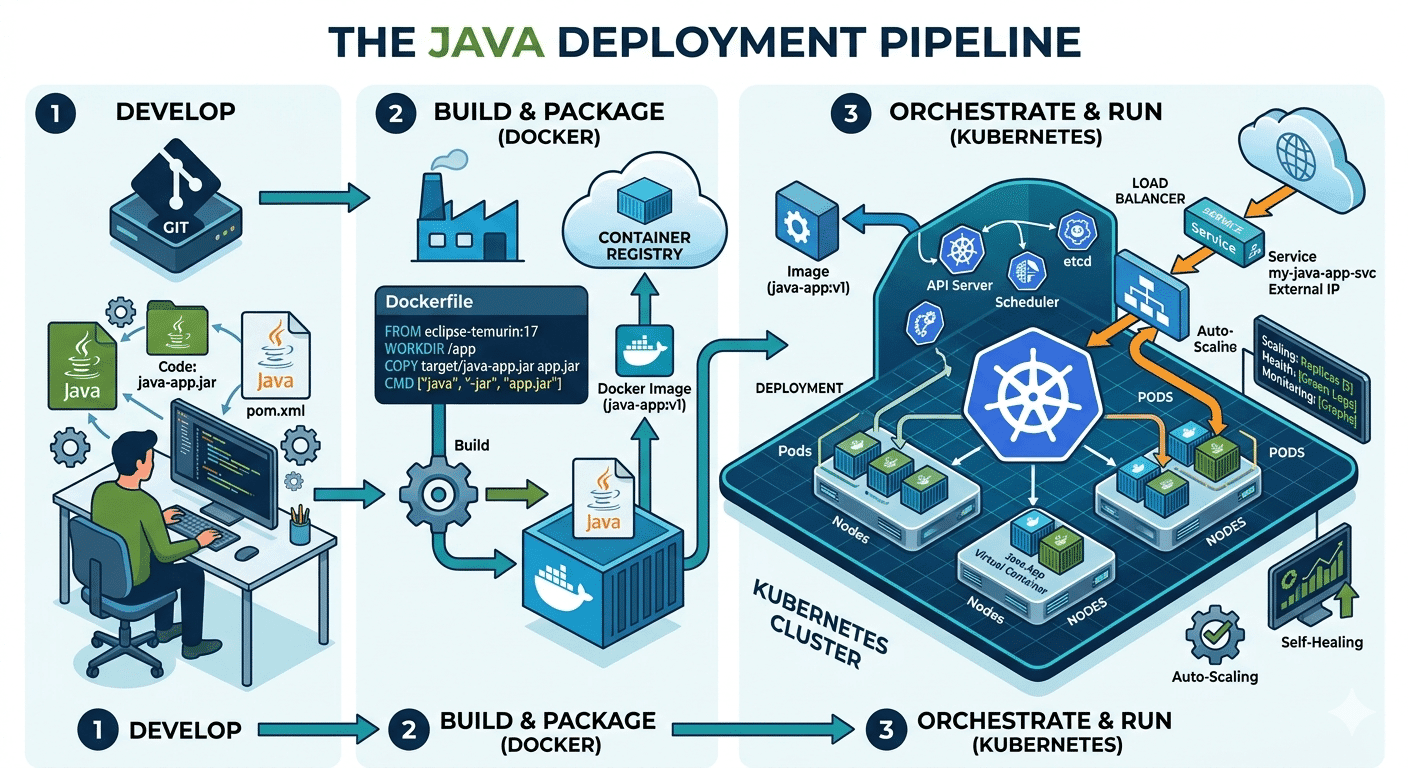
How Do Java Development Teams Use Docker and Kubernetes to Deploy Applications?
Last updated on: April 24, 2026Posted by: ExamRadar
AI vs Machine Learning: Key Differences Every Professional Should Know
Last updated on: February 13, 2026Posted by: ExamRadar